CVE-2026-114938 (Java4Shell): Remote code execution vulnerability in OpenJDK
Published: November 17, 2026 at 9pm PT
Last updated: November 18, 2026 at 6:45pm PT
CVE ID: CVE-2026-114938
Severity: Oracle assigned a High severity rating (8.1 on CVSS 3.1), while the discovering security researchers at Calif assigned a Critical severity rating (9.2 on CVSS 4.0).
Summary:
CVE-2026-114938, known as Java4Shell, is a critical memory-corruption flaw in the Base64 decoder in OpenJDK. It could allow an unauthenticated attacker to execute code on systems running affected Java versions. Oracle released fixed builds on November 17, and CISA has urged organizations to patch immediately.
Absolute product status:
Customer Action:
If you are a Secure Endpoint, FirmGuard, or Syxsense customer, no action is required. These products are not vulnerable.
If you are a Secure Access SaaS customer, no action is required. Absolute is deploying necessary patches as outlined above and will update this advisory and notify customers when they are complete.
If you are a Secure Access On-Premises customer and using server with vulnerable CPU architecture, we recommend you deploy the update we will be providing as soon as possible. We will update this advisory and notify customers when the update is released and available for download.
You may also apply an interim mitigation by:
1- Setting system environment variable on affected servers by opening ‘System Properties’ or ‘View advanced system properties’ and edit the system environment variables:
JAVA_TOOL_OPTIONS
-XX:+UnlockDiagnosticVMOptions -XX:-UseBASE64Intrinsics
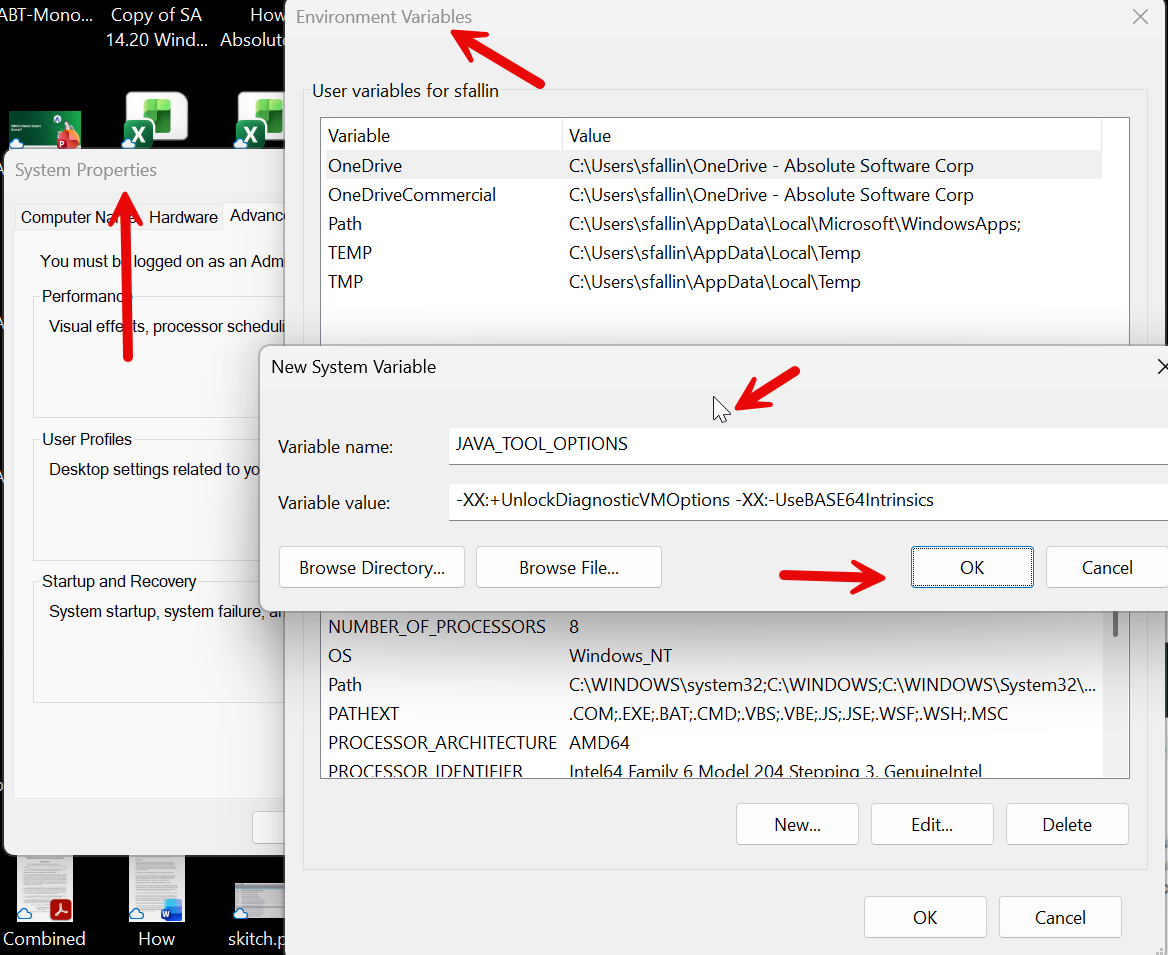
2- Reboot the servers.
For other solutions you may have deployed, identify affected systems: Java4Shell is in the Java runtime itself, so dependency scanners may not flag it. Check every host, container image, and application that bundles its own Java runtime.
- Run java -version on each system and compare against vendor guidance.
- Reported affected versions: OpenJDK 17.0.6 and later, plus 21, 25, and 27, on x86-64 processors with AVX-512 VBMI support.
- Reported not affected: ARM64 systems, and standard Java 8 and 11 builds. Oracle’s Java 8 performance build is reported as an exception.
- Confirm all of the above against the Oracle and OpenJDK advisories.
Check for signs of compromise.
Look for:
- unexpected crashes or restarts of Java services
- unusual child processes spawned by Java processes
- unexpected outbound connections from Java hosts
No exploitation in the wild had been reported as of November 17.
What you should do:
- Inventory all Java runtimes in your environment, including bundled copies and container images.
- Apply the fixed builds from your Java vendor. Oracle’s are available now, and other OpenJDK vendors are rolling theirs out.
- Review logs from the date above for the indicators listed.
- Return to this page for updates on Absolute products.
How Absolute can help:
Resilience for Security, Resilience for Automation, and Syxsense customers can scan for vulnerable endpoint and server instances and apply the applicable vendor patches for Oracle Java, Amazon Corretto, and Azul Zulu deployments. We will also enable patching for Red Hat and Microsoft OpenJDK deployments when patches are available from the vendors.
For Resilience customers, we also plan to release a REACH script that can scan for vulnerable instances and will update this advisory and notify customers when it is available.
Timeline of updates:
- November 17, 2026, 9pm PT
- November 17, 2026, 11pm PT
- November 18, 2026, 3pm PT: Advisory published (v1.1).
- November 18, 2026, 6:45pm PT: Advisory Published (v1.2)
References:
- CISA alert: https://www.cisa.gov/news-events/alerts/2026/11/17/critical-java-vulnerability-requires-immediate-patching
- Oracle Critical Patch Update: https://www.oracle.com/security-alerts/cspunov2026.html#AppendixJAVA
- OpenJDK advisory: https://openjdk.org/groups/vulnerability/advisories/2026-11-17