Compliance Reporting That Closes What It Finds
The problem
A report that just shows you a problem isn’t done — it’s the start of a manual process: find the devices, open a ticket, track it down, hope someone follows through.
A finding isn’t a fix. It’s a to-do list.
A compliance finding is only useful if something happens next. The real work — and the real risk — lives in the gap between knowing about a problem and actually closing it.

Nobody gets credit for knowing about a problem. You get credit for fixing it. Our reporting is built around that difference.
Always audit-ready. Compliance that maintains itself.
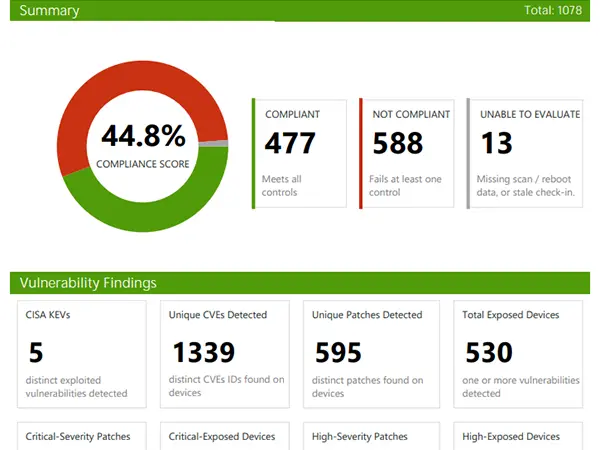
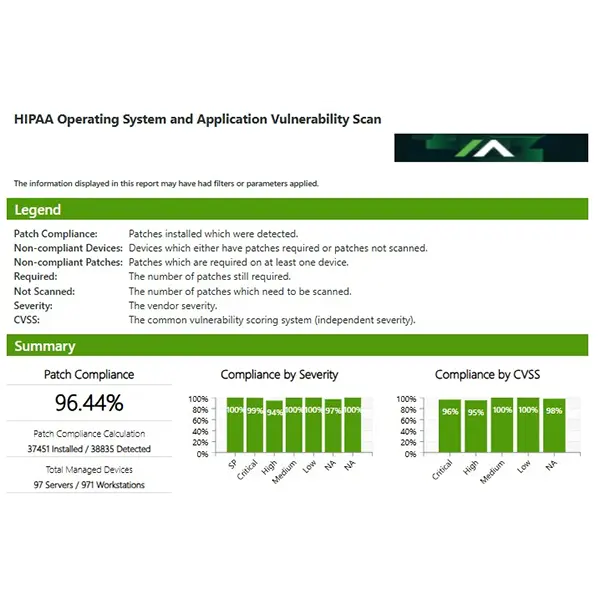
Set your compliance policies once, and Absolute Workflows — each with a self-updating target list already built in — run continuously in the background, remediating drift automatically. The report becomes a byproduct: always accurate, always audit-ready, with no work on your part. Want to double-check first? Drill into that same query behind any report to see the exact devices before you remediate. The same model extends across CIS, PCI DSS, HIPAA, and SOX compliance reports, plus vulnerability and patch-risk reporting by device, family, and vulnerability.
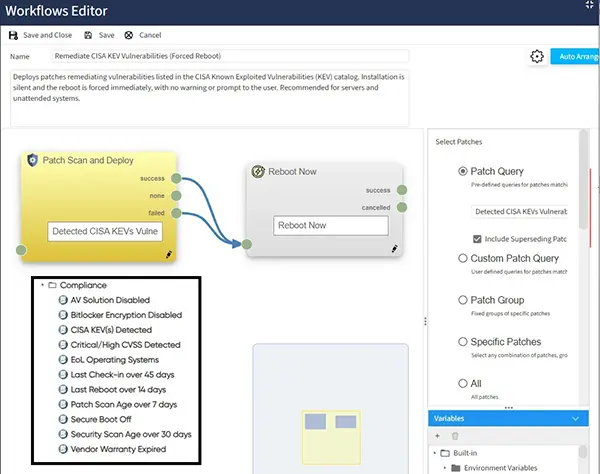
Essential capabilities for compliance reporting
Prebuilt CIS Benchmark, PCI DSS, HIPAA, and SOX reports — audit-ready, no manual assembly.
Fixes trigger the moment drift is detected — no waiting for the next scan or review cycle.
Policies run in the background at all times, closing the gap between finding and fixing before it widens.
Powered by Endpoint Analytics’ unprecedented telemetry — operational, security, and resilience data, all in one place.
Patch and vulnerability reports surface confirmed active exploits ahead of CVSS severity alone.
Track resolved vulnerabilities by name, so you can prove what was fixed, not just what was found.
Customizable dashboards track compliance and application trends out of the box, and the Absolute AI Assistant answers questions in plain language.
Knowing what to fix first is the whole game
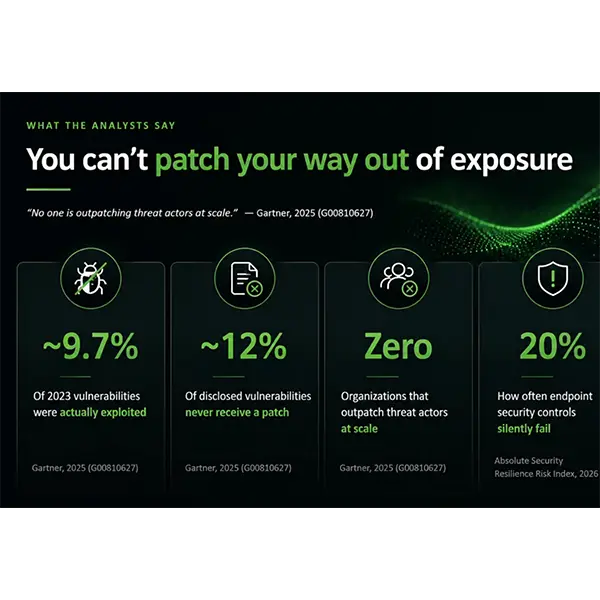
Endpoint control failure is inevitable. Resilience comes from closing the remediation gap — knowing what to fix first, fixing it fast, proving it worked, and recovering quickly.
- See how leading teams prioritize what actually matters.
- Learn what “proving it worked” looks like in practice.
The Report Is Proof Compliance Is Automatic
See how the same reports that prove compliance are also the reason nothing’s out of compliance in the first place.
- See the breadth: CIS, PCI DSS, HIPAA, SOX, and vulnerability reporting, prebuilt.
- Automate your fleet: Check out the Absolute Workflows behind every report — set once, runs continuously.
- Know what matters most is handled first: KEV-confirmed exploits are prioritized ahead of everything else.
Go deeper on compliance and reporting
Reporting FAQs
CIS Benchmark, PCI DSS, HIPAA, and SOX reports come prebuilt, alongside patch and vulnerability reporting by device, family, or vulnerability.
Every report draws on Endpoint Analytics’ three-tier telemetry — operational, security, and resilience data — for a fuller picture than compliance status alone.
Yes. Compliance Overview covers your most vulnerable areas at a glance. Use the matching query to review the exact devices, or go directly to setting a matching policy for any category that’s non-compliant.
No. Absolute Workflows remediate automatically, and stop targeting a device the moment it’s compliant.
Findings confirmed as actively exploited (CISA KEV) are surfaced and prioritized ahead of CVSS severity scores alone.
Reports make you audit-ready. Automation runs continuously underneath them, steadily finding issues and fixing them — so you’re not just compliant on paper, you’re secure and ready for what comes next.