

Absolute + SentinelOne: Protection That Comes Back
Eles agem à velocidade das máquinas. Nós travamos o tempo de inatividade.
Como a Absolute e a SentinelOne trabalham melhor em conjunto

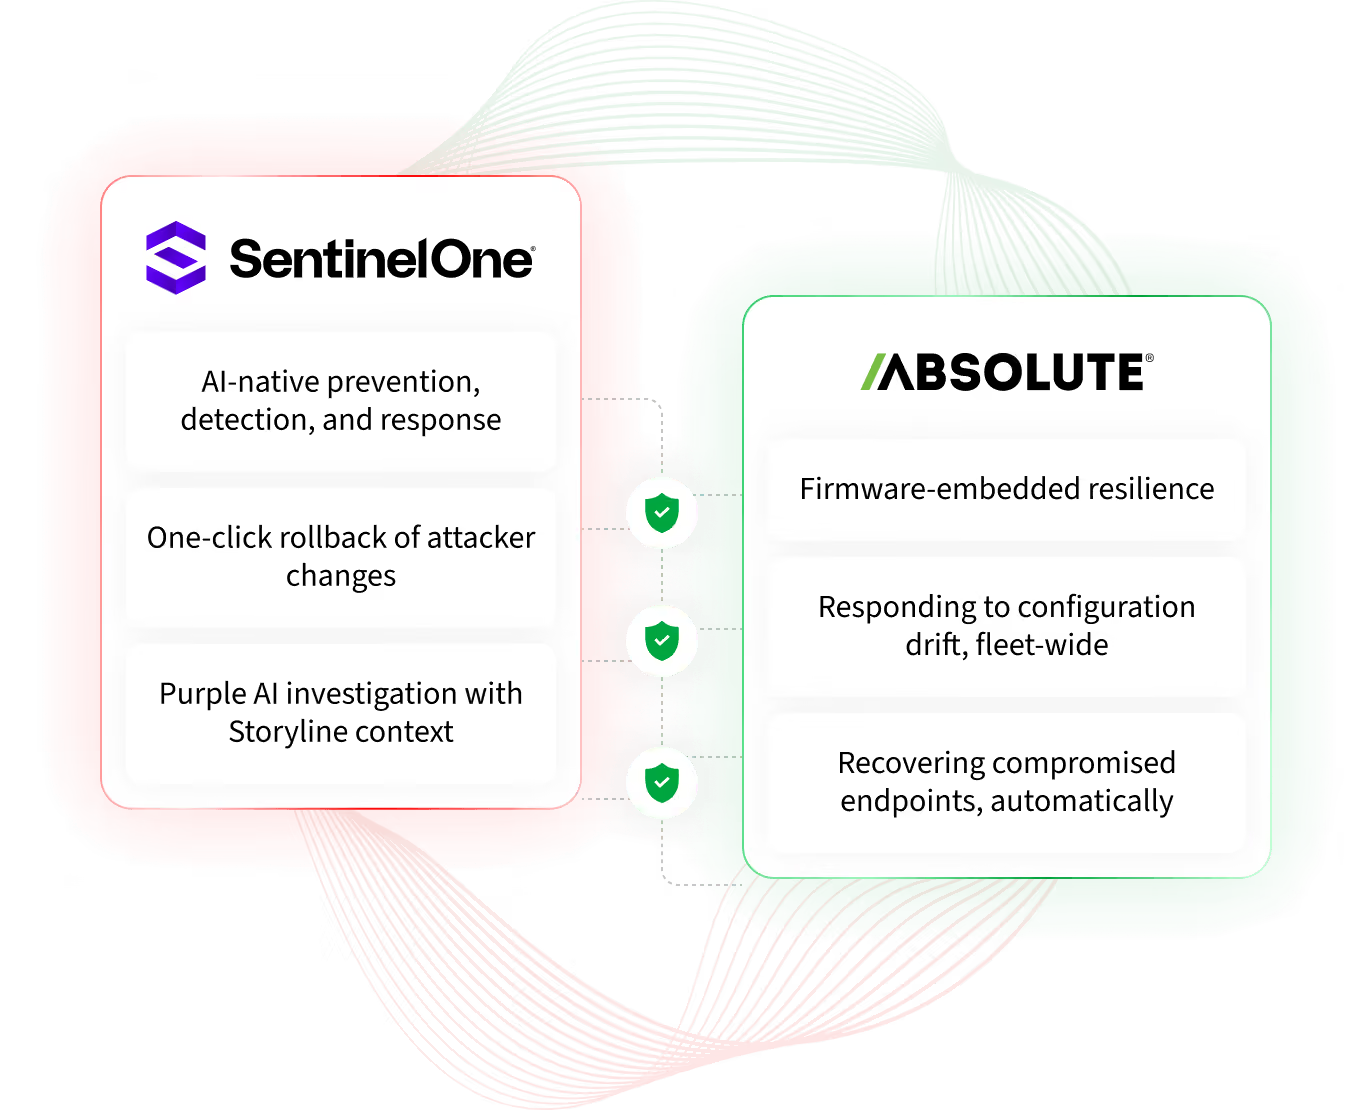
Keep SentinelOne running, even when attackers target it
Mapped to the Cyber Resilience Framework
Gartner's model for building cyber resilience — anticipate, withstand, recover, and adapt — maps to how SentinelOne and Absolute work, with both contributing to every phase at once.
Anticipate
Behavioral AI and Purple AI surface anomalous endpoint activity so analysts can act before it becomes an incident.
Absolute continuously monitors the health of the SentinelOne agent and other controls, flagging drift or failure before it creates a blind spot.
You see both what attackers are doing and whether your defenses are healthy enough to stop them.
Withstand
AI-native prevention, detection, and response through a single agent stops attacks at machine speed, with decisions made locally.
Absolute Persistence keeps a firmware-level channel to the device that stays available even when attackers go after security tools directly.
An attack that disables the agent becomes a temporary gap, not a lasting blind spot.
Recover
Storyline and Purple AI reconstruct what happened, and one-click rollback undoes attacker changes on a running system.
Absolute Resilience reinstalls the SentinelOne agent if it's removed, and Rehydrate lets IT restore devices whose OS won't boot.
SentinelOne rolls back the attack; Absolute brings back the agent and the device, so recovery doesn't stall.
Adapt
Behavioral AI models are retrained against newly observed attacker tradecraft, so prevention keeps pace with attackers.
Absolute's telemetry gives security and IT teams the fleet-wide data to see what failed, why, and where policy needs to change.
Each incident informs both sides: how attackers operated and which defenses held, so the next response is faster.
Concept per Gartner, “Gartner’s Cyber Resilience Framework: Anticipate, Withstand, Recover and Adapt,” Arthur Sivanathan, Lampis Alevizos, Phillip Shattan, Richard Addiscott, 21 May 2026, ID G00843075. GARTNER is a registered trademark and service mark of Gartner, Inc. and/or its affiliates in the U.S. and internationally and is used herein with permission. All rights reserved.
An attacker disables SentinelOne. Here's what happens next.
The agent is shut down
An attacker with admin rights uses a vulnerable driver to stop the SentinelOne agent and blind the device.
Absolute sees the gap
Absolute's next health check finds the agent stopped and flags the device, even though the OS looks normal.
The agent comes back
Absolute Resilience repairs the agent or reinstalls a verified copy, per your policy, with no one touching the device.
Protection and visibility return
SentinelOne resumes defending the device at machine speed, and the attacker's window closes.